
Thought Leadership & Knowledge Hub
Podcast RSS FeedKnowledge Hub
Strategic perspectives, credit risk methodologies, audit standards, and cyber resilience intelligence for enterprise decision-makers.

Featured Publication•Enterprise Risk Management
Mozambique Courts South African Energy Investment: Cross-Border Gas Security & Infrastructure Risk
As Mozambique’s state oil firm ENH courts South African energy giant Sasol and regional partners for new natural gas developments—alongside Eni’s 6-well drilling campaign for Coral North FLNG—Southern Africa faces a critical cross-border infrastructure transition. Here is how corporate boards must manage off-taker concentration, transit security, and transition finance risks.
Enterprise Risk Management
6 min read•Nay & Joe Risk Team
As Mozambique’s state oil firm ENH courts South African energy giant Sasol and regional partners for new natural gas developments—alongside Eni’s 6-well drilling campaign for Coral North FLNG—Southern Africa faces a critical cross-border infrastructure transition. Here is how corporate boards must manage off-taker concentration, transit security, and transition finance risks.

Credit Risk & IFRS 9
6 min read•Nay & Joe Risk Team
Senegal’s successful mobilization of $582 million (350 billion CFA francs) in the regional WAEMU bond market marks a decisive strategic pivot away from expensive, dollar-denominated Eurobonds following domestic fiscal audit disclosures. Here is how sovereign domestic borrowing alters commercial bank balance sheets, liquidity risk, and IFRS 9 staging across West Africa.

Enterprise Risk Management
6 min read•Nay & Joe Risk Team
High-level central banker warnings in mid-October 2026 highlight a new macroeconomic reality: the trillion-dollar global scramble for AI data centers, specialized silicon, and energy grids is absorbing liquid capital and stoking supply-side inflation. Here is why the AI infrastructure boom forces African enterprise CIOs and CFOs to re-evaluate tech investments and capital expenditure models.

Audit & Compliance
6 min read•Nay & Joe Risk Team
With the World Bank setting a target to quintuple critical minerals financing and the Africa Finance Corporation (AFC) pouring direct capital into uranium, iron ore, and copper processing, African resource corridors are entering a transformative era. Here is how mining boards, joint ventures, and host governments must navigate strict ESG covenants, in-country beneficiation mandates, and geopolitical compliance.

Audit & Compliance
6 min read•Nay & Joe Risk Team
The Africa Centres for Disease Control and Prevention’s disclosure that over $700 million in emergency health response funds deployed in the DRC cannot be accounted for marks an unprecedented crisis governance failure. For corporate and public sector audit committees, the crisis proves why manual controls collapse during emergencies. Here is how organizations must digitize internal audit controls.
Credit Risk & IFRS 9
6 min read•Nay & Joe Risk Team
The sharp disagreement between the Nigerian Ministry of Finance and the World Bank over a reported 124% debt-service-to-revenue ratio in H1 2026 highlights an urgent challenge for risk officers: how to measure sovereign credit risk accurately when official accounting scopes diverge. Here is how financial institutions must recalibrate sovereign debt models and IFRS 9 staging triggers.

Enterprise Risk Management
6 min read•Nay & Joe Risk Team
Having mobilized over ₦4.65 trillion in primary equity during Nigeria's 24-month banking recapitalization drive, the Central Bank of Nigeria has officially shifted gears. Static, uniform minimum capital thresholds are being replaced by an individualized Risk-Based Capital Framework. Here is what bank executive committees and risk leaders must implement.

Cybersecurity
6 min read•Nay & Joe Risk Team
The Nigerian Communications Commission’s nationwide rollout of its Device Verification System (*315#)—with a strict 30-day disconnection window for non-compliant hardware—presents a major operational and fraud risk for the nation’s payment ecosystem. Here is how FinTech operators, agent banking networks, and banks must secure their terminal supply chains.

Enterprise Risk Management
6 min read•Nay & Joe Risk Team
As the European Bank for Reconstruction and Development (EBRD) funds major smart grid and digital metering deployments to slash ATC&C losses across Nigerian DisCos, proposed amendments to the Electricity Act have triggered governance friction between state electricity commissions and NERC. Here is how utility financiers, off-takers, and corporate boards must navigate the power regulatory divide.

Credit Risk & IFRS 9
6 min read•Nay & Joe Risk Team
With commercial lending rates hovering near 28%–32% and industrial performance falling 10% in recent business confidence monitors, Nigerian manufacturers face a severe working capital squeeze. Compounded by conflicting regulatory oversight between state electricity commissions and NERC, industrial balance sheets must pivot from survival to strategic restructuring. Here is the executive guide.
Enterprise Risk Management
6 min read•Nay & Joe Risk Team
As Airtel Africa advances the standalone listing of its multi-billion-dollar mobile commerce business on the London Stock Exchange, African fintech enters a new governance era. Carving out a mobile money operator across 14 sovereign African markets creates unprecedented operational, regulatory, and valuation challenges.

Enterprise Risk Management
5 min read•Nay & Joe Risk Team
When energy regulators in East Africa raised domestic fuel prices this week in response to Middle East shipping tensions and escalating landed petroleum import benchmarks, the ripple hit far beyond the petrol pump. Corporate balance sheets, long-term transport contracts, and commercial bank loan portfolios under IFRS 9 are facing sudden margin compression.
Credit Risk & IFRS 9
5 min read•Nay & Joe Risk Team
Many corporate treasurers and CFOs across Southern Africa budgeted for aggressive central bank interest rate cuts in late 2026. This week, South African Reserve Bank (SARB) Governor Lesetja Kganyago shattered those assumptions, warning that energy and food cost pressures mean inflation risks remain decisively on the upside.
Audit & Compliance
6 min read•Nay & Joe Risk Team
Shell agreement this week to sell its Nigerian domestic gas business to Vaaris Energy marks another landmark chapter in the structural transfer of strategic onshore energy assets to local operators. While celebrating indigenous participation, boards, financiers, and regulators must navigate severe technical, environmental decommissioning, and power-sector off-take risks.
Credit Risk & IFRS 9
6 min read•Nay & Joe Risk Team
Gabon successful pricing this week of an 8-year, $580 million Eurobond with a 9.375% coupon proves that international capital markets remain open to transitional African sovereigns. But borrowing in US dollars near double-digit interest rates imposes a rigorous fiscal and financial burden on domestic economies.
Audit & Compliance
6 min read•Nay & Joe Risk Team
Abu Dhabi International Resources Holding (IRH) confirmed this week that it is negotiating to acquire additional copper and critical mineral mining assets in Zambia. As Gulf sovereign wealth funds accelerate their deployment across Africa’s energy transition corridors, corporate boards and joint-venture partners must navigate a new era of geopolitical, ESG, and local beneficiation governance.
Credit Risk & IFRS 9
6 min read•Nay & Joe Risk Team
The launch of the Africa Credit Rating Agency (AfCRA) on October 7, 2026, is not just international diplomacy. When global rating agencies downgrade an African nation, it inflates borrowing costs, weakens local currencies, and forces commercial banks to charge local businesses 30% interest. Here is how AfCRA changes the game.

Audit & Compliance
5 min read•Nay & Joe Risk Team
For decades, corporate directors and C-suite officers assumed company insurance and legal shields would protect their personal assets. Today, regulators are imposing direct criminal penalties, director disqualifications, and bonus clawbacks for risk oversight failures. Here is what directors must do.
Enterprise Risk Management
5 min read•Nay & Joe Risk Team
Passing an annual compliance audit no longer saves your company when systems crash. Regulators and boardrooms are retiring static GRC in favor of GRR — Governance, Risk, and Resilience. Here is what that means in practice.
Cybersecurity
5 min read•Nay & Joe Risk Team
Telling your board that a vulnerability is "High Risk" or "Amber" tells them almost nothing. Cyber Risk Quantification (CRQ) translates technical vulnerabilities into expected monetary loss, enabling executives to allocate budgets where they actually protect the balance sheet.

Enterprise Risk Management
5 min read•Nay & Joe Risk Team
Moving everything to the public cloud was supposed to save money. For African enterprises and global businesses facing foreign exchange shocks and multi-hour outages, cloud bills exploded by 300%. Here is why smart CTOs are bringing core workloads back to on-premise servers.

Audit & Compliance
5 min read•Nay & Joe Risk Team
You think your enterprise is diversified because you use 20 different fintech, software, and IT vendors. But if 18 of them run on the exact same cloud server farm or single payment switch, you have zero redundancy. Here is how 4th-party concentration risk threatens business continuity.
Credit Risk & IFRS 9
5 min read•Nay & Joe Risk Team
The Pan-African Payment and Settlement System (PAPSS) promises to eliminate dollar intermediation for intra-African trade. But for treasury, credit, and risk teams, it introduces new settlement risk, FX exposure, and counterparty default dynamics that most organisations are not yet prepared for.
Credit Risk & IFRS 9
4 min read•Nay & Joe Risk Team
Nigeria has one of the world's most sophisticated digital identity ecosystems — NIN, BVN, and now the proposed National Digital Identity Platform. But most financial institutions are still underusing these assets. The banks that learn to embed identity verification into dynamic credit scoring will leave the rest behind.
Enterprise Risk Management
5 min read•Nay & Joe Risk Team
Nigeria's agent banking network has grown to over 1.4 million POS agents. It is also one of the fastest-growing fraud surfaces in African financial services. Understanding the operational risk mechanics — SIM-swap, ghost agents, and transaction laundering — is now a board-level risk conversation.

Cybersecurity
4 min read•Nay & Joe Risk Team
Nigerian small and medium enterprises are increasingly targeted by cybercriminals — not because they have more money than large banks, but because they have weaker defences. The good news: the most effective protections are free or very cheap. Here's exactly what to do.
Credit Risk & IFRS 9
5 min read•Nay & Joe Risk Team
The CBN's Open Banking Regulatory Framework is now operational. For Nigerian banks, fintechs, and their risk teams, this changes the game on data sharing, credit underwriting, and fraud liability. Here's what every risk professional needs to understand before their institution falls behind.
Credit Risk & IFRS 9
3 min read•Nay & Joe Risk Team
In volatile economic conditions, relying on annual audited financial statements to evaluate borrower or vendor creditworthiness creates a dangerous time-lag in risk identification.

Enterprise Risk Management
3 min read•Nay & Joe Risk Team
Many enterprise Risk Appetite Statements sit as passive, Board-approved documents that fail to influence daily operational and lending decisions on the ground.

Audit & Compliance
3 min read•Nay & Joe Risk Team
Automated credit scoring engines, IFRS 9 ECL models, and risk rating algorithms naturally degrade over time ("model drift") as economic conditions evolve.
Enterprise Risk Management
3 min read•Nay & Joe Risk Team
Business Email Compromise (BEC) and vendor invoice manipulation are frequently misdiagnosed as purely "IT security bugs," when they are actually operational risk failures in internal financial controls.
Enterprise Risk Management
3 min read•Nay & Joe Risk Team
Financial institutions and enterprises are relying on a shrinking number of dominant cloud and SaaS providers, creating severe vendor concentration risk.

Enterprise Risk Management
3 min read•Nay & Joe Risk Team
Employees are increasingly using consumer AI tools and unsanctioned SaaS applications to accelerate daily work without IT or Risk department approval.
Enterprise Risk Management
3 min read•Nay & Joe Risk Team
Organizations waste 20% to 30% of their annual IT budget on unused SaaS licenses, unattached cloud storage volumes, and redundant software subscriptions.
Enterprise Risk Management
3 min read•Nay & Joe Risk Team
Many IT departments possess thick Disaster Recovery (DR) binders that pass compliance audits, but fail disastrously during real-world outages because they never test live failovers under pressure.

Cybersecurity
3 min read•Nay & Joe Risk Team
Cybercriminals are upgrading to autonomous "agentic AI" that evaluates target networks and executes multi-step attacks without human intervention.

Enterprise Risk Management
3 min read•Nay & Joe Risk Team
Attackers are bypassing complex employee phishing campaigns and targeting corporate VPNs, firewalls, and gateway appliances directly.

Audit & Compliance
3 min read•Nay & Joe Risk Team
An AI tool is dangerous when it has the technical authority to delete files, approve invoices, or alter customer records without human approval.

Enterprise Risk Management
3 min read•Nay & Joe Risk Team
Companies spend millions on shiny new security tools, while hackers enter through forgotten 5-year-old test servers or legacy email portals.

Cybersecurity
3 min read•Nay & Joe Risk Team
Massive dark web dumps of stolen corporate credentials mean attackers do not need to hack into your system; they can buy valid logins online.
Credit Risk & IFRS 9
3 min read•Nay & Joe Risk Team
Regulators are clarifying that board members do not need technical IT backgrounds; they must measure business impact, downtime, and recovery.

Cybersecurity
3 min read•Nay & Joe Risk Team
As businesses rush to give AI tools access to emails and files, the risk of an AI making a costly, unauthorized decision is skyrocketing.

Enterprise Risk Management
3 min read•Nay & Joe Risk Team
Hackers are using AI to find and exploit known flaws faster than human IT teams can install updates. Prioritization is the new perimeter.

Cybersecurity
3 min read•Nay & Joe Risk Team
Cybercriminals are no longer guessing passwords; they are stealing session tokens to bypass Multi-Factor Authentication entirely.

Enterprise Risk Management
3 min read•Nay & Joe Risk Team
A breach at a single software supplier can automatically infect hundreds of their clients via routine, forced software updates.

Cybersecurity
3 min read•Nay & Joe Risk Team
Scammers are using Generative AI to create flawless, highly personalized fake emails and voice clones of executives.

Cybersecurity
3 min read•Nay & Joe Risk Team
The U.S. government issued an urgent warning regarding severe security flaws in Linux, an operating system powering global cloud infrastructure.
Enterprise Risk Management
7 min read•Nay & Joe Risk Team
Navigating state-owned utility offtaker defaults, currency convertibility risks, and political risk insurance structures under the African Continental Free Trade Area.
Audit & Compliance
6 min read•Nay & Joe Risk Team
Securing pan-African digital payment rails, API payment gateways, and Nigeria Data Protection Act compliance against real-time transfer fraud and insider vulnerabilities.
Credit Risk & IFRS 9
7 min read•Nay & Joe Risk Team
Assessing foreign exchange rate adjustments, risk-weighted asset (RWA) inflation, and forward-looking credit loss staging under the Central Bank of Nigeria recapitalization directives.

Credit Risk & IFRS 9
7 min read•Nay & Joe Risk Team
Evaluating agricultural trade credit risk, crop collateral impairment under severe weather events, and Stage 2 IFRS 9 ECL modeling for commodity lenders.

Audit & Compliance
6 min read•Nay & Joe Risk Team
Securing genomic datasets, Phase II/III clinical trial integrity, and CRO third-party APIs against advanced persistent threats and regulatory non-compliance.
Enterprise Risk Management
6 min read•Nay & Joe Risk Team
Navigating fourth-party cloud vendor outages, SaaS vendor financial distress, and escrow data recovery under ISO 31000 & DORA operational resilience rules.

Cybersecurity
7 min read•Nay & Joe Risk Team
Mitigating ground station command injection, satellite bus firmware tampering, and orbital telemetry spoofing in low-Earth orbit (LEO) commercial broadband networks.

Credit Risk & IFRS 9
6 min read•Nay & Joe Risk Team
Evaluating aircraft residual value impairments, airline lease default probabilities, and IFRS 9 Stage 2 migration triggers for commercial aircraft lessors and financiers.
Credit Risk & IFRS 9
7 min read•Nay & Joe Risk Team
Assessing working capital drain, raw material price volatility, and Stage 2 IFRS 9 ECL triggers across Tier-1 and sub-tier EV battery supply chain counterparties.

Cybersecurity
7 min read•Nay & Joe Risk Team
Securing virtualized telecommunications core networks and multi-tenant slice isolation against rogue API signaling attacks and zero-trust cloud vulnerabilities.
Credit Risk & IFRS 9
6 min read•Nay & Joe Risk Team
Assessing trade credit default risk, fuel transition capital requirements, and Stage 2 ECL triggers in global maritime logistics and freight forwarders.

Audit & Compliance
6 min read•Nay & Joe Risk Team
Split-second fraud mitigation requirements, bank liability shifts for victim reimbursement, and real-time AI transaction monitoring architectures.

Credit Risk & IFRS 9
7 min read•Nay & Joe Risk Team
Property valuation recalibration, Debt Service Coverage Ratio (DSCR) stress tests, and Stage 3 impairment reserves ahead of the commercial debt wall.

Cybersecurity
6 min read•Nay & Joe Risk Team
Supply chain cyber assessments, Controlled Unclassified Information (CUI) encryption, and zero-trust vendor audits across defense sub-contractors.

Enterprise Risk Management
6 min read•Nay & Joe Risk Team
Algorithmic liability allocation, sensor spoofing cyber insurance, and ISO 31000 risk appetite boundaries for commercial autonomous fleets.

Enterprise Risk Management
6 min read•Nay & Joe Risk Team
Deploying AI clinical diagnostic tools requires balancing diagnostic innovation with strict HIPAA, NDPA 2023, and medical device data privacy controls.
Cybersecurity
6 min read•Nay & Joe Risk Team
Protecting energy grids and power utilities requires securing legacy SCADA systems, industrial IoT gateways, and IT-OT network convergence under NIST SP 800-82.

Audit & Compliance
5 min read•Nay & Joe Risk Team
FinCEN and U.S. banking regulators issue joint guidance clarifying SAR confidentiality boundaries vs. customer communication during fraud investigations.
Credit Risk & IFRS 9
6 min read•Nay & Joe Risk Team
OSFI defers Guideline B-6 and Credit Risk Management releases to 2027 while reinforcing baseline Liquidity Adequacy Requirements (LAR) and model recalibration.

Credit Risk & IFRS 9
6 min read•Nay & Joe Risk Team
With $1.4 trillion in private debt maturing through 2027, direct lenders transition from rapid deal origination to intensive workouts and obligor risk rating.
Cybersecurity
6 min read•Nay & Joe Risk Team
The Financial Stability Board warns G20 leaders on autonomous Frontier AI cyber threats, mandating upstream safety controls and bare-metal recovery.
Cybersecurity
5 min read•Nay & Joe Risk Team
OpenAI launches $1B Daybreak initiative providing subsidized defensive AI threat analysis models to community banks and credit unions.

Enterprise Risk Management
6 min read•Nay & Joe Risk Team
European Supervisory Authorities active DORA enforcement mandates fourth-party vendor mapping, threat scanning, and 72-hour breach reporting.

Cybersecurity
6 min read•Nay & Joe Risk Team
NIST finalizes FIPS 203 ML-KEM quantum-safe standards. Discover how financial institutions build crypto-agility to mitigate Harvest-Now, Decrypt-Later risks.

Enterprise Risk Management
6 min read•Nay & Joe Risk Team
Autonomous AI agents executing multi-step API actions create a critical governance gap. Learn how to implement cryptographically bound identities and Zero-Trust safeguards.
Credit Risk & IFRS 9
5 min read•Nay & Joe Risk Team
With heightened regulatory scrutiny on asset derecognition and settlement timing, learn how automated credit engines eliminate reporting distortions and Stage 2 ECL spikes.
Cybersecurity
6 min read•Nay & Joe Risk Team
Regulatory authorities enforce mandatory 36-hour breach notification windows. Discover how to build an operational human firewall against AI phishing.
Credit Risk & IFRS 9
6 min read•Nay & Joe Risk Team
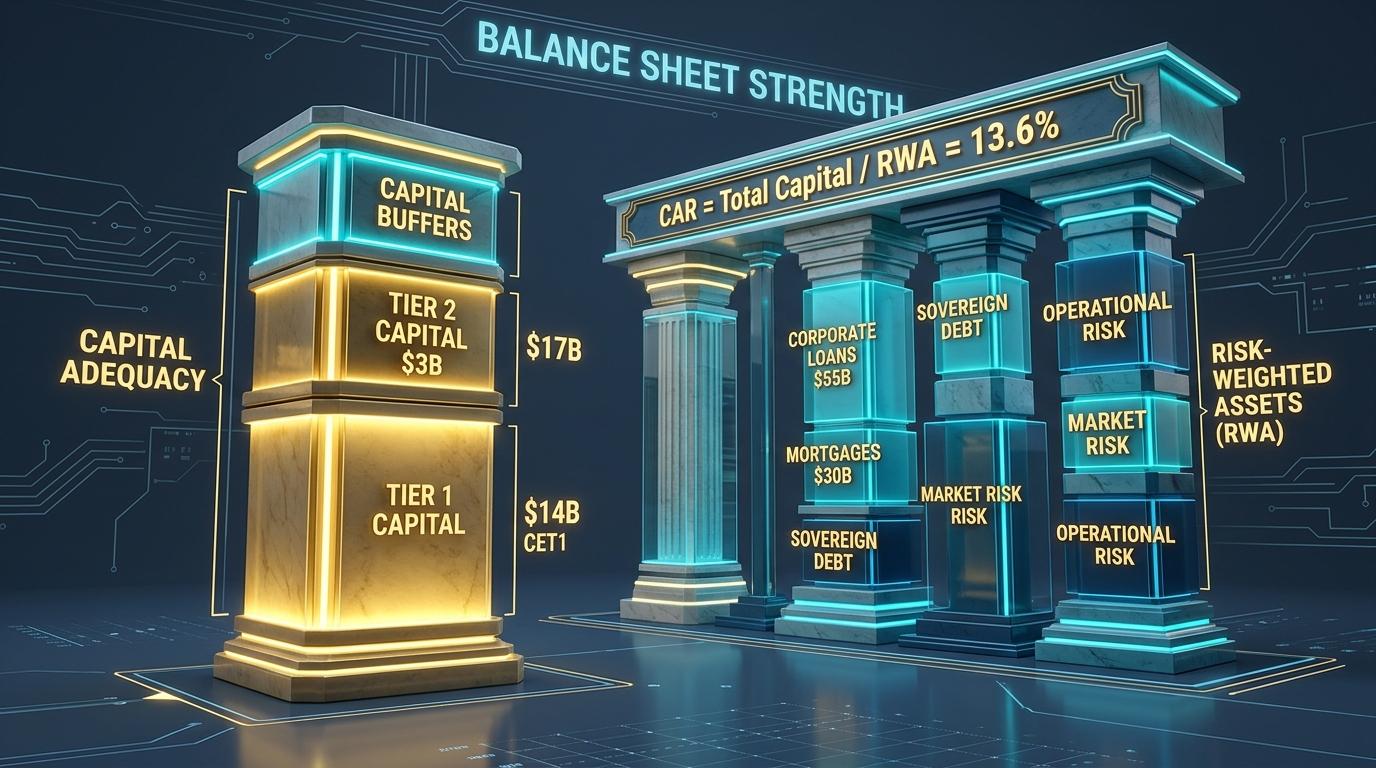
As global banking agencies finalize Basel III capital proposals, learn how credit risk committees balance capital adequacy reserves with loan portfolio growth.
Enterprise Risk Management
6 min read•Nay & Joe Risk Team
Central banks tighten supervisory oversight on algorithmic lending. Discover the 4 pillars of AI model explainability, bias auditing, and human-in-the-loop controls.
Audit & Compliance
6 min read•Nay & Joe Risk Team
With international digital product security mandates taking effect, learn how internal auditors audit software bills of materials (SBOM) and cloud vendor access.
Cybersecurity
6 min read•Nay & Joe Risk Team
Over 68% of all enterprise breaches involve a human element. Discover how leading organisations shift from passive compliance to active security accountability.
Cybersecurity
5 min read•Nay & Joe Risk Team
Cyber hygiene is built on daily habits, not periodic grand gestures. Explore the 5 foundational habits that reduce your attack surface by over 90%.
Cybersecurity
6 min read•Nay & Joe Risk Team
Your network is the central nervous system of your business. Learn how firewalls, ZTNA, and intelligent traffic monitoring protect against lateral movement.
Cybersecurity
5 min read•Nay & Joe Risk Team
An unlocked workstation or an unencrypted backup drive can bypass millions in digital security. Discover how physical controls protect digital assets.
Cybersecurity
6 min read•Nay & Joe Risk Team
Data is your organization's lifeblood. Learn how data classification, cloud storage governance, and encryption safeguard sensitive information.
Cybersecurity
6 min read•Nay & Joe Risk Team
Threats move in hours, not annual review cycles. Discover how continuous vulnerability management and threat intelligence keep you ahead of adversaries.
Cybersecurity
7 min read•Nay & Joe Risk Team
What separates resilient organisations from broken ones is response. Learn how to structure, test, and execute a high-impact Incident Response plan.
Cybersecurity
6 min read•Nay & Joe Risk Team
Smartphones, laptops, and contractor devices form your new security perimeter. Explore EDR, MDM, and Zero Trust endpoint strategies.
Cybersecurity
6 min read•Nay & Joe Risk Team
Cloud providers secure the infrastructure — you secure your data and configurations. Avoid misconfiguration breaches with CSPM and IAM governance.
Cybersecurity
5 min read•Nay & Joe Risk Team
Policies aren't bureaucracy — they are guardrails translating risk appetite into action. Learn how to write clear, measurable, and enforceable security policies.
Cybersecurity
6 min read•Nay & Joe Risk Team
Security culture is what happens when no one is watching. Learn how psychological safety and leadership modeling transform security into a shared mission.
Cybersecurity
6 min read•Nay & Joe Risk Team
You cannot eliminate all risk — nor should you try. Learn how to align likelihood and impact with board-approved risk appetite frameworks.
Cybersecurity
6 min read•Nay & Joe Risk Team
Security audits are your organization's mirror. Explore vulnerability scans, penetration tests, and red team exercises.
Cybersecurity
6 min read•Nay & Joe Risk Team
AI phishing, quantum threats, and supply chain attacks are changing the game. Learn why core security principles remain your best defense.
Cybersecurity
5 min read•Nay & Joe Risk Team
Event Viewer, Task Scheduler, and Resource Monitor are built-in security sensors available on every Windows desktop.
Cybersecurity
5 min read•Nay & Joe Risk Team
Deleting a file does not erase it. Learn certified data destruction methods (ATA Secure Erase, Cryptographic Erasure) for end-of-life hardware.
Cybersecurity
5 min read•Nay & Joe Risk Team
OS security isn't just about patches — it's about posture. Discover BIOS/UEFI boot integrity and driver signing verification.
Cybersecurity
5 min read•Nay & Joe Risk Team
VirusTotal and Google Safe Browsing put fast, multi-engine threat analysis in every employee's hands.
Cybersecurity
5 min read•Nay & Joe Risk Team
Unpatched software, excessive privileges, and unvetted PDF tools create low-hanging fruit for attackers. Learn modern AppSec hygiene.
Cybersecurity
5 min read•Nay & Joe Risk Team
MDE provides cloud-powered EDR, automated incident investigation, and device isolation. Learn how to operationalize your alerts.
Cybersecurity
5 min read•Nay & Joe Risk Team
Network Access Control (NAC) enforces Zero Trust at the gate, ensuring unpatched or unencrypted devices cannot enter corporate networks.
Cybersecurity
5 min read•Nay & Joe Risk Team
Access should be earned, not instant. Incorporate mandatory security quizzes and policy sign-offs into your onboarding workflow.
Cybersecurity
5 min read•Nay & Joe Risk Team
Personal smartphones and home PCs are compliance minefields. Establish strict browser-only policies for unmanaged hardware.
Cybersecurity
5 min read•Nay & Joe Risk Team
Cutting unnecessary external email traffic reduces phishing vectors. Shift internal collaboration to encrypted Teams/SharePoint channels.
Credit Risk & IFRS 9
7 min read•Nay & Joe Risk Team
IFRS 9 is a strategic credit surveillance tool, not just an accounting hurdle. Explore staging migration, data engineering bottlenecks, and forward-looking portfolio intelligence.
Credit Risk & IFRS 9
7 min read•Nay & Joe Risk Team
Relying on spreadsheets and subjective credit officer reviews creates dangerous blind spots. Discover how multi-dimensional Obligor Risk Rating (ORR) engines objectify credit assessments.
Audit & Compliance
7 min read•Nay & Joe Risk Team
Internal audit must evolve from periodic checklist exercises to dynamic, risk-aligned assurance. Learn how audit digitization elevates auditors into strategic advisors.
Enterprise Risk Management
6 min read•Nay & Joe Risk Team
Static Excel risk registers give the feeling of managing risk without the substance. Learn how continuous Key Risk Indicator (KRI) monitoring transforms ERM.
Enterprise Risk Management
6 min read•Nay & Joe Risk Team
Spreadsheet-based ERM hits an operational ceiling as enterprises grow. Discover why centralized risk registers and automated scoring are essential for board oversight.
Credit Risk & IFRS 9
7 min read•Nay & Joe Risk Team
Selecting credit risk technology requires rigorous evaluation beyond vendor slides. Learn how 30-day Proof of Concept (POC) deployments validate performance.
Subscribe to Risk Intelligence Briefings
Get weekly executive summaries on credit risk modelling, IFRS 9 regulatory standards, cybersecurity threats, and enterprise risk strategies. Zero spam.